Free Palo Alto Networks NetSec-Architect Exam Practice Questions
Palo Alto Networks Network Security Architect
Total Questions: 45Focus Only on What Matters For Palo Alto Networks NetSec-Architect Exam Preparation
Many candidates desire to prepare their Palo Alto Networks NetSec-Architect exam with the help of only updated and relevant study material. But during their research, they usually waste most of their valuable time with information that is either not relevant or outdated. Study4Exam has a fantastic team of subject-matter experts that make sure you always get the most up-to-date preparatory material. Whenever there is a change in the syllabus of the Palo Alto Networks Network Security Architect exam, our team of experts updates NetSec-Architect questions and eliminates outdated questions. In this way, we save you money and time.
Palo Alto Networks NetSec-Architect Exam Sample Questions & Answers
A global organization is upgrading its data-center and private-cloud infrastructure. The environment includes:
A Nutanix AHV cluster that hosts critical east-west application workloads
A VMware ESXi cluster with multi-socket hosts that supports high-throughput workloads (>10 Gbps)
A new pair of PA-5450 firewalls to secure the perimeter and perform encrypted-traffic inspection at scale
Strict performance service-level agreements (SLAs) for both north-south and east-west traffic, with heavy dependence on TLS 1.3 and IPSec
A Network Functions Virtualization (NFV) environment on KVM that delivers high-performance security services to maximize packet throughput and minimize latency
The chief architect must ensure that the firewall design prevents hypervisor contention, optimizes non-uniform memory access (NUMA), and uses hardware capabilities for encrypted traffic.
VM-Series on Nutanix AHV - Resource Allocation
Because the Nutanix cluster is already heavily utilized, the architect's primary concern is avoiding performance degradation of the virtual firewall. Thin provisioning or ballooning could add latency and unpredictability, which is unacceptable for a security-sensitive workload.
VM-Series on VMware ESXi - NUMA and vCPU Placement
In the VMware ESXi environment, the architect is deploying VM-Series for workloads exceeding 10 Gbps. Placing vCPUs across NUMA nodes or oversubscribing cores would cause latency through cross-socket memory access and scheduling delays. Likewise, dedicating logical hyperthreads does not deliver the deterministic data-plane performance required.
Operational Integration and High Availability
With performance assured through correct hypervisor and hardware provisioning, the architect also evaluates high availability (HA). VM-Series pairs are deployed in active/passive HA across Nutanix and VMware clusters, while PA-5450s provide the data center's north-south secure-perimeter deployment. This provides resilience without adding unnecessary east-west inspection bottlenecks.
The recommendation must be a scalable, high-performance firewall deployment that aligns with enterprise SLAs and the CISO's encrypted-traffic concerns.
To optimize throughput and minimize latency, what is recommended for configuring vCPUs and NUMA in this deployment?
A global manufacturing organization has a strategic plan for rapid growth through mergers and acquisitions. Several deployments acquired by the organization are considered large, with existing IP address schemas and allocations that conflict with those of the parent organization. The manufacturing organization needs access to the resources before a re-IP initiative can be completed.
All deployments include a variety of IoT devices. Leadership requires protection of vulnerable assets and identification of any known CVEs associated with the IoT devices. The governance, risk, and compliance (GRC) team requires comprehensive, non-repudiable logs to identify all IoT devices reporting "Critical (9.0+) CVE scores" for mandatory remediation.
Throughput must exceed the current 1 Gbps trending rate and, with anticipated growth, will soon scale to 5 Gbps.
Segmentation is mandatory, with enclaves based on region, device type, and function.
Which off-ramp should an architect recommend to meet the organization's requirements?
A global manufacturing organization has a strategic plan for rapid growth through mergers and acquisitions. Several components acquired by the organization are considered large deployments with existing IP address schemas and allocations that conflict with those of the parent organization. The manufacturing organization requires access to the resources before a re-IP initiative can be completed.
All deployments contain a variety of IoT devices. Leadership requires protection of vulnerable assets and identification of any known CVEs associated with the IoT devices. The governance, risk, and compliance (GRC) team requires comprehensive, non-repudiable logs to identify every IoT device reporting "Critical (9.0+) CVE scores" for mandatory remediation.
Throughput must exceed the current 1 Gbps trending rate and, with anticipated growth, will soon scale to 5 Gbps.
Segmentation is mandatory, with enclaves based on region, device type, and function.
A firewall has been configured in tap mode to provide traffic visibility for profiling. Inconsistencies in profiling have been observed, with a mix of behaviors.
What are two possible root causes of this behavior? (Choose two.)
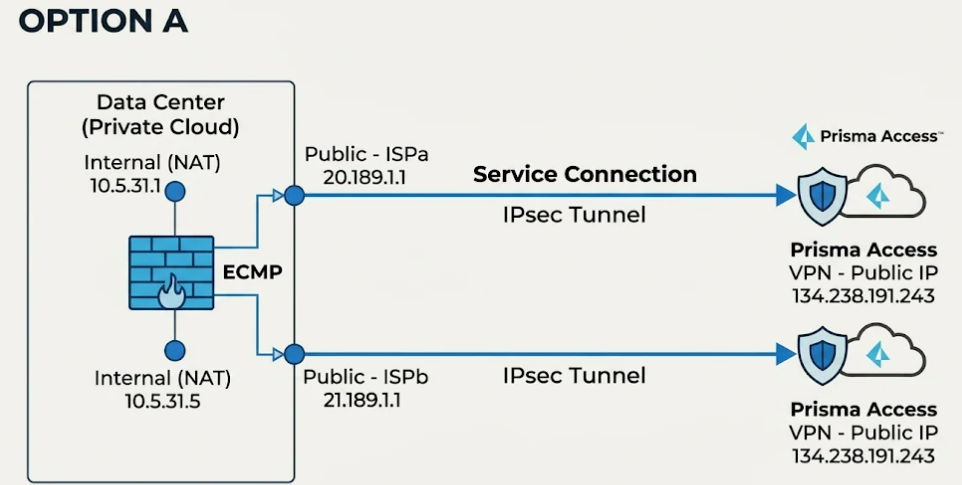
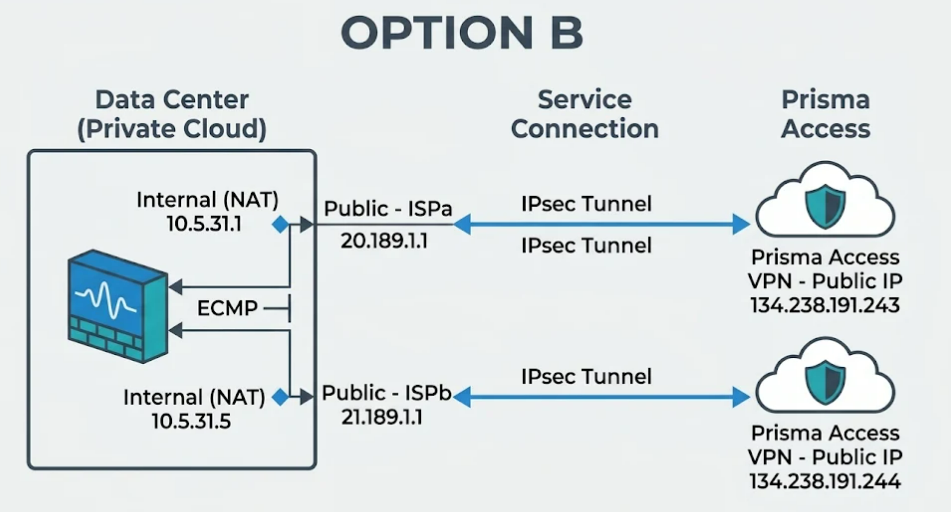
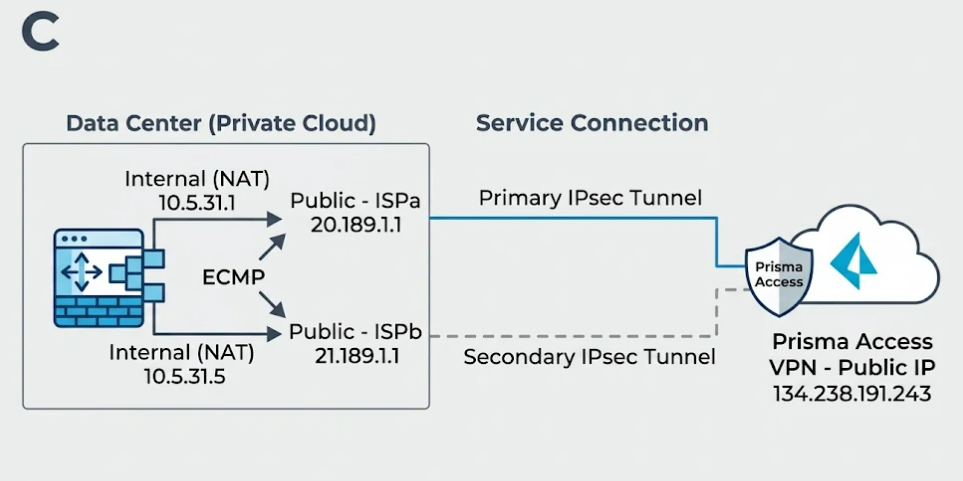
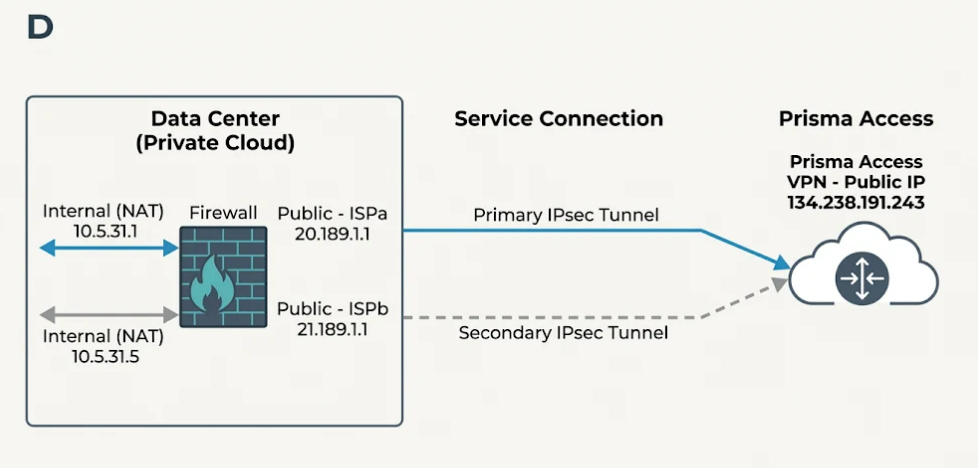
An organization is designing Prisma Access service connections for its data centers. Each data center has redundant 10 Gb internet links and must support at least 1.5 Gbps of throughput for Prisma Access-connected users and branches.
Which diagram shows a solution that satisfies these use-case requirements?
A global organization is securing critical applications during a cloud-based migration to a cloud-first design. It is currently performing a brownfield migration of its most critical applications---such as CRM and product intellectual property / design systems---into Azure Cloud. The organization already has an active/passive high-availability (HA) NGFW deployed at its data center with multiple zones, and it has replicated that design in its existing Azure HA deployment.
The organization recognizes the need to modernize its security posture as critical workloads move out of the data center and users connect from anywhere. Its security model follows a traditional ''hard shell, soft center'' approach:
Zero Trust Gaps -
Current network segmentation is perimeter-based. The organization wants to extend Zero Trust principles across cloud and on-premises environments.
The network depends heavily on VLANs and IP address-based Access Control Lists (ACLs), segmented primarily by office location and broad departmental groups.
Once employees are on the corporate network (that is, inside the ''perimeter''), they have relatively broad access.
If attackers compromise one endpoint (for example, through a phishing email), they can readily move laterally and scan for high-value targets.
Cloud Blind Spots -
The organization uses Azure for its production environments and hosts applications containing sensitive customer data.
Cloud security controls are often managed independently from the on-premises network. Access is frequently granted through overly permissive identity and access management (IAM) roles and keys based on the resource instead of the user's real-time context or application health.
Remote User Access -
Many remote users still hairpin through the corporate data center merely to access internet or SaaS resources, causing latency and inefficiency.
Traditional VPN is used for remote employees.
The VPN grants access to the entire internal network segment, making the remote endpoint the new, weaker perimeter. There is no continuous check of the user's device health after the initial connection.
Visibility and Logging -
Logs are mainly stored on-premises and then forwarded to a local Security Information and Event Management (SIEM) solution. As applications move to Azure, visibility into cloud traffic and user behavior becomes fragmented.
Data Security Concern -
Sensitive data, including product design files, will now reside in SaaS and cloud environments. The organization requires data security to prevent leakage and enforce compliance.
Ingress Security -
Third-party partners and suppliers need access into the data center and cloud applications, creating risk at ingress points.
The current Microsoft Azure NGFW architecture will not support the increased traffic from the newly migrated applications.
Which architectural solution will provide scalable inspection?

Review details
Country · 1 review
Currently there are no comments in this discussion, be the first to comment!